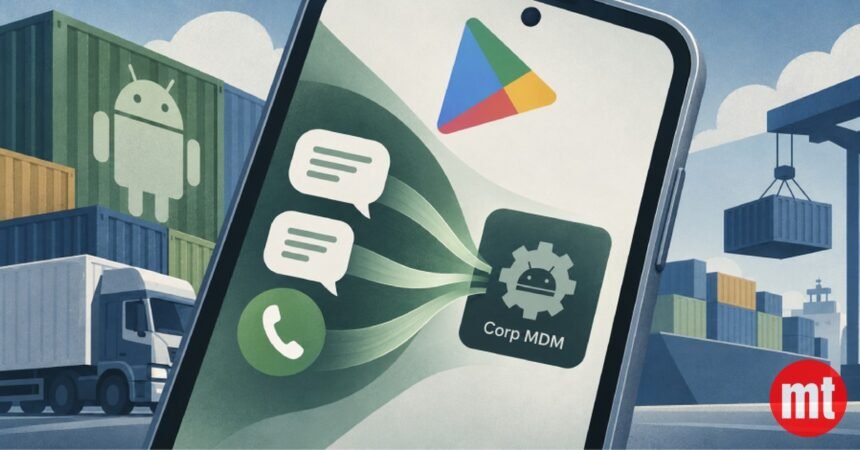
Android spyware logistics India is now a confirmed threat vector, with a new malware strain called Corp MDM actively targeting freight and supply chain companies through fake app storefronts. Researchers at Have I Been Squatted flagged the campaign in September 2026. The spyware intercepts SMS messages and redirects live phone calls without the victim’s knowledge.
What You Need To Know
- Corp MDM spyware impersonates CEVA Logistics and TKW Logistics apps to gain device access
- The malicious APK uses the package name “com.corp.mdm” disguised as a system service
- The campaign uses cloned Google Play pages to distribute the infected Android Package Kit files
- Capabilities confirmed: real-time SMS theft and live call redirection on infected Android devices
How Android Spyware Logistics India Campaign Uses Fake Play Store Pages
Security researchers at Have I Been Squatted identified the Corp MDM operation after detecting spoofed Google Play storefronts in September 2026. The fake pages mimic two real freight brands, CEVA Logistics and TKW Logistics, to earn user trust before delivering a malicious APK file. Once installed, the app registers itself under the package name “com.corp.mdm” and presents as a routine system service, making it nearly invisible to the average employee on a corporate handset. The Android spyware logistics India threat is now classified as an active campaign, not a proof-of-concept.
Why Indian Logistics Firms Face the Sharpest Exposure Right Now
India’s freight sector runs on Android. Warehouse staff, last-mile delivery riders, and fleet dispatchers overwhelmingly use low-to-mid-range Android handsets that rarely receive timely security patches. Companies like Delhivery, Ecom Express, and Blue Dart operate hundreds of thousands of field agents who depend on messaging apps and voice calls to coordinate shipments daily. The Android spyware logistics India campaign is purpose-built to exploit exactly this operational dependency, harvesting OTPs, shipment codes, and client communications before the victim notices anything wrong.
The business consequences extend beyond data loss. Intercepted SMS messages can expose two-factor authentication tokens tied to banking and customs portals. Redirected calls create openings for business email compromise and fraudulent payment rerouting. Indian logistics firms processed over 5 billion shipments in fiscal year 2026, and a significant portion of those transactions flow through SMS-based confirmation chains that Corp MDM can silently monitor. Even a single compromised operations manager device puts an entire regional hub’s communications at risk.
“Logistics companies sit on a goldmine of real-time financial and identity data, and most of them are defending it with consumer-grade mobile security. Corp MDM is a precision strike at that gap.” — Cybersecurity Analyst, Enterprise Mobile Sector
What Happens Next as Security Teams Race to Contain the Threat
Mobile device management vendors are expected to push emergency detection signatures within days of the September 2026 disclosure. IT teams at logistics firms must immediately audit any APK installed outside the official Google Play Store and cross-reference package names against the confirmed “com.corp.mdm” identifier. The broader Android spyware logistics India risk will persist as long as sideloading remains common practice in the sector. CERT-In has not yet issued a formal advisory, but one is widely anticipated given the campaign’s scale and the sensitivity of the targeted industry.
Sources: TRAI ↗ | ITU ↗ | COAI ↗ Have I Been Squatted (September 2026 threat disclosure); The Hacker News, “Corp MDM Spyware Targets Logistics Firms, Steals New SMS and Redirects Calls,” https://thehackernews.com/2026/09/corp-mdm-spyware-targets-logistics.html
People Also Ask
- What is Corp MDM spyware and how does it affect Android spyware logistics India targets? Corp MDM is a malicious Android app that disguises itself as a system service. It steals incoming SMS messages and redirects phone calls, giving attackers access to OTPs, shipment data, and confidential client communications on infected logistics employee devices.
- How does Corp MDM spyware get installed on Android phones in India? Attackers clone legitimate Google Play Store pages for brands like CEVA Logistics and TKW Logistics. Workers download what appears to be an official company app, but the APK installs the Corp MDM payload under a fake system service name instead.
- How can Indian logistics companies protect their Android devices from Corp MDM spyware? IT administrators should immediately ban APK sideloading on all corporate handsets, audit installed packages for “com.corp.mdm,” enforce mobile device management policies, and monitor CERT-In advisories for official guidance expected following the September 2026 disclosure.