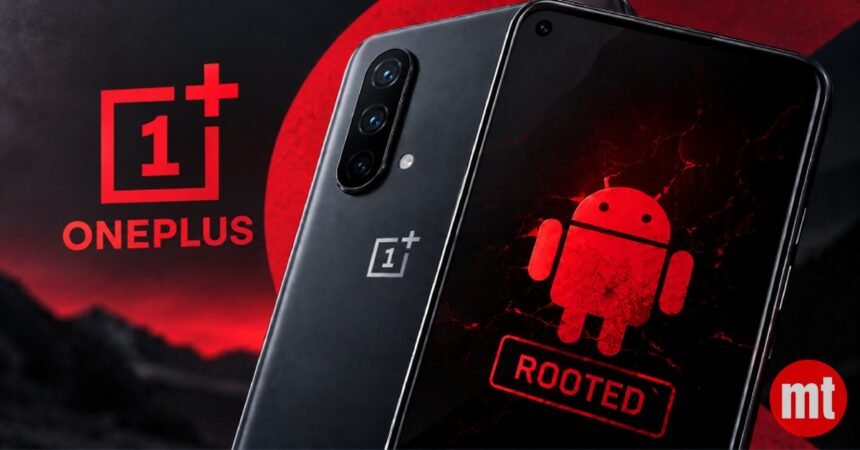
A confirmed OnePlus root vulnerability lets any installed Android app seize complete control of a OnePlus 15 without requesting a single special permission. Security researcher Rasmus Moorats published findings this week showing two chained flaws in OxygenOS hand root access to attackers. OnePlus has confirmed the vulnerability remains unpatched.
What You Need To Know
- Researcher Rasmus Moorats chained 2 OxygenOS flaws to achieve full root access on a OnePlus 15
- A malicious app needs zero special Android permissions to exploit the vulnerability
- OnePlus confirmed the same flaws affect multiple OPPO devices as well
- No patch has been released as of September 2026
OnePlus Root Vulnerability: How 2 OxygenOS Flaws Open the Door to Full Device Takeover
The OnePlus root vulnerability was discovered by Estonian security researcher Rasmus Moorats, who published his findings in September 2026. Moorats chained two separate bugs in OnePlus’s own OxygenOS software on a fully updated OnePlus 15 to achieve root access, the highest possible privilege level on an Android device. Root access lets an attacker read all data, install persistent malware, disable security features, and intercept encrypted communications. No third-party library or system-level permission was required to trigger the exploit chain.
Why Is This OnePlus Root Vulnerability Especially Dangerous for Indian Users?
India is one of OnePlus’s largest and most loyal markets, with millions of OnePlus 15 units sold since the device launched in early 2026. The OnePlus root vulnerability strikes at the heart of that install base. Indian users rely on OxygenOS devices for mobile banking, UPI payments through apps like PhonePe and Google Pay, and sensitive corporate communications. A zero-permission exploit means even a sideloaded game or a fake productivity app from a third-party APK store can silently root the device without triggering any Android permission dialog.
Beyond individual users, Indian enterprises that have deployed OnePlus or OPPO handsets under BYOD policies face an immediate compliance risk. OnePlus confirmed to Moorats that the two flaws extend across several of its own device lines and OPPO-branded phones. OPPO India commands a substantial share of the mid-range segment. Security teams at Indian companies cannot rely on Mobile Device Management software alone to detect an exploit that operates at root level, sitting above the visibility of most MDM agents currently deployed in corporate fleets.
“An exploit that asks for no permissions and still achieves root is a worst-case scenario for enterprise security teams. Every day without a patch is another day attackers can build weaponised APKs and push them through fake app listings.” — Cybersecurity Analyst, Telecom Sector
What Happens Next: No Patch Timeline, No CVE Score Yet
As of publication in September 2026, OnePlus has not released a patch, a CVE identifier, or a public security advisory for the OnePlus root vulnerability. Moorats followed responsible disclosure protocols and gave OnePlus advance notice before going public. Users running a OnePlus 15 or any OPPO device on the affected firmware should avoid installing apps from outside the Google Play Store immediately. Security researchers are urging OnePlus to issue an emergency OxygenOS update and publish a full list of affected device models without further delay.
Sources: DOT ↗ | ITU ↗ | COAI ↗ The Hacker News (https://thehackernews.com/2026/09/unpatched-oneplus-flaws-let-installed.html); Rasmus Moorats security disclosure, September 2026
People Also Ask
- What is the OnePlus root vulnerability discovered in 2026? Security researcher Rasmus Moorats found two chained flaws in OxygenOS that allow any installed Android app to gain root access on a OnePlus 15 without requesting any special permissions, giving attackers full device control.
- Which OnePlus and OPPO devices are affected by this root exploit? OnePlus confirmed the vulnerability extends beyond the OnePlus 15 to multiple other OnePlus and OPPO devices. A complete list of affected models has not been publicly released by the company as of September 2026.
- How can OnePlus users protect themselves until a patch is released? Avoid installing apps from outside the Google Play Store, remove unfamiliar sideloaded apps immediately, and monitor OnePlus’s official security bulletin page for an emergency OxygenOS firmware update.